HOMESERVICESVIGOR SHIELD DrayTek VigorShield Threat Protection Guardian (1 year)

DrayTek VigorShield Threat Protection Guardian (1 year)
*****
SKU: 4711637181111
CONTACT US FOR PROJECT PRICES
 +30 210 6777007
 info@draytek.gr
DrayTek Threat Protection
DrayTek Threat Protection is an advanced subscription-based cybersecurity service within VigorShield, available for selected Vigor router models. It provides multi-layered network-level protection by leveraging AI-assisted threat detection, behavior-based analysis, URL/IP Reputation and cloud-based threat intelligence to protect the router, local network and connected devices against modern cyber threats.
By combining gateway-level protection with continuous network behavior analysis and cloud intelligence, Threat Protection enhances network security without requiring an additional security appliance or complex deployment.
The service operates agentlessly, with no additional software required on network devices. This allows it to protect devices where endpoint security cannot normally be installed, such as IP cameras, POS systems, printers and IoT devices.
Multi-Layered Network Protection
Threat Protection combines multiple security mechanisms to protect the router and devices connected to the LAN.
Router Protection (Edge Gateway Security) – protects the router as the central entry point to the network with DoS/DDoS attack mitigation, Port Scan detection & blocking, brute-force attack protection, as well as blocking of malicious IP addresses and suspicious network traffic.
Network & Device Protection – automatically identifies connected devices and continuously monitors their behavior to detect abnormal or malicious activity.
AI-assisted Threat Detection – uses AI-assisted and behavior-based mechanisms to identify suspicious network behavior and potential threats.
Suspicious Device Isolation – enables the immediate isolation of suspicious or compromised devices, helping prevent a potential threat from spreading across the rest of the network.
IoT & Unmanaged Device Protection – identifies and protects IoT and unmanaged devices that do not have their own antivirus or endpoint security, using behavior-based anomaly detection and network-level protection against exploit and injection attacks.
URL/IP Reputation
URL/IP Reputation is included with the Threat Protection subscription and uses continuously updated threat intelligence data to assess the reputation of websites, domains and IP addresses.
This enables the router to identify and block communication with malicious or high-risk destinations, helping protect the network against phishing, malware, ransomware, botnets and other online threats. Protection is applied at gateway level, without requiring software to be installed on each endpoint.
Safe Browsing & Content Filtering
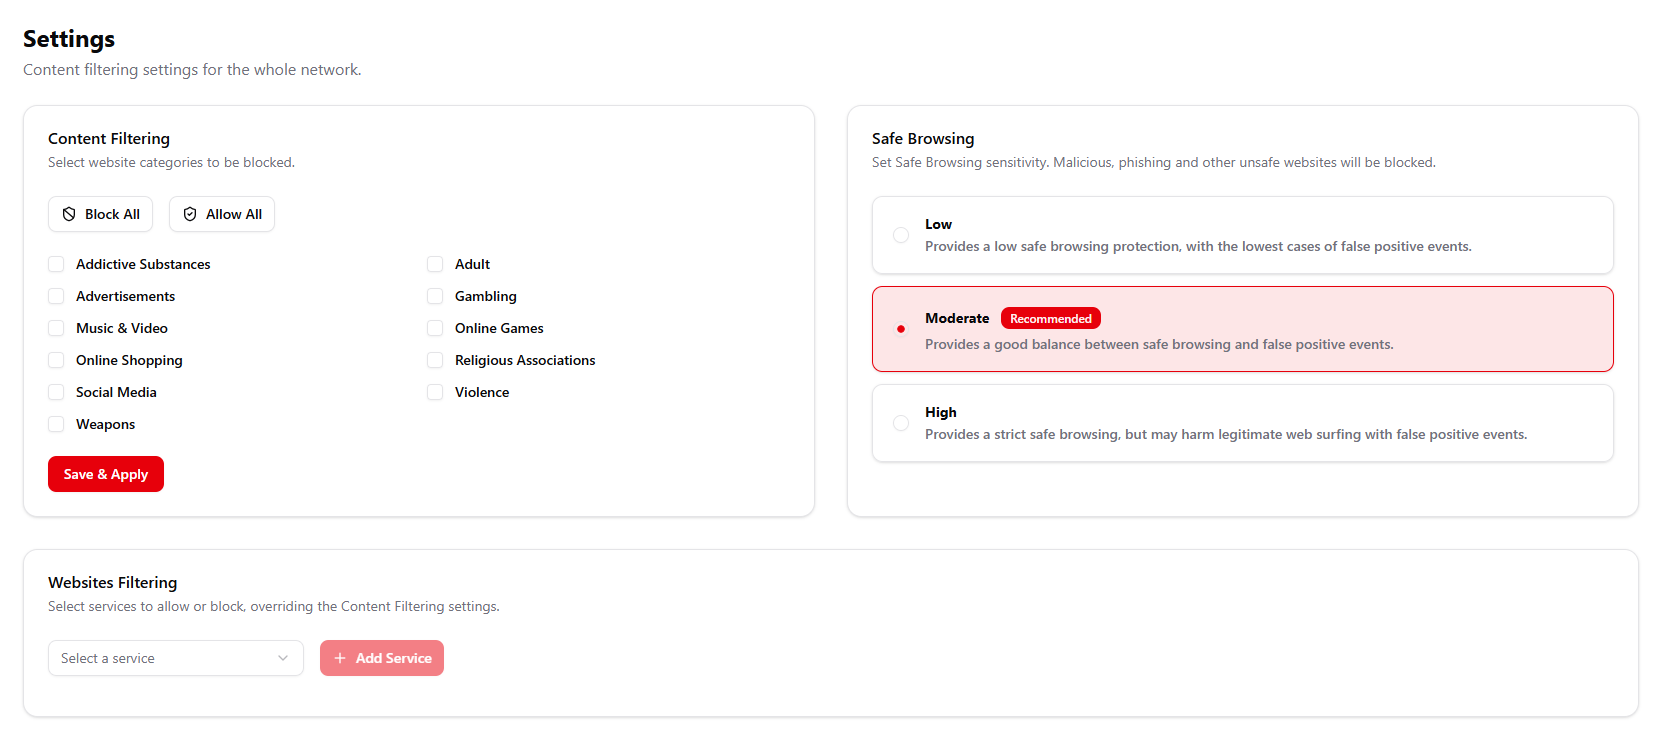
Threat Protection provides Safe Browsing to help protect users against malicious, phishing and other unsafe websites. The administrator can select the required protection level through three sensitivity settings: Low, Moderate and High, depending on the network's requirements and security policy.
Content Filtering also enables administrators to control access to websites based on categories such as Social Media, Online Shopping, Online Games, Gambling, Advertisements, Music & Video and more.
Custom rules can also be created for specific websites and services, allowing them to be permitted or blocked independently of the general Content Filtering settings.
Cloud Monitoring, Visibility & Reporting
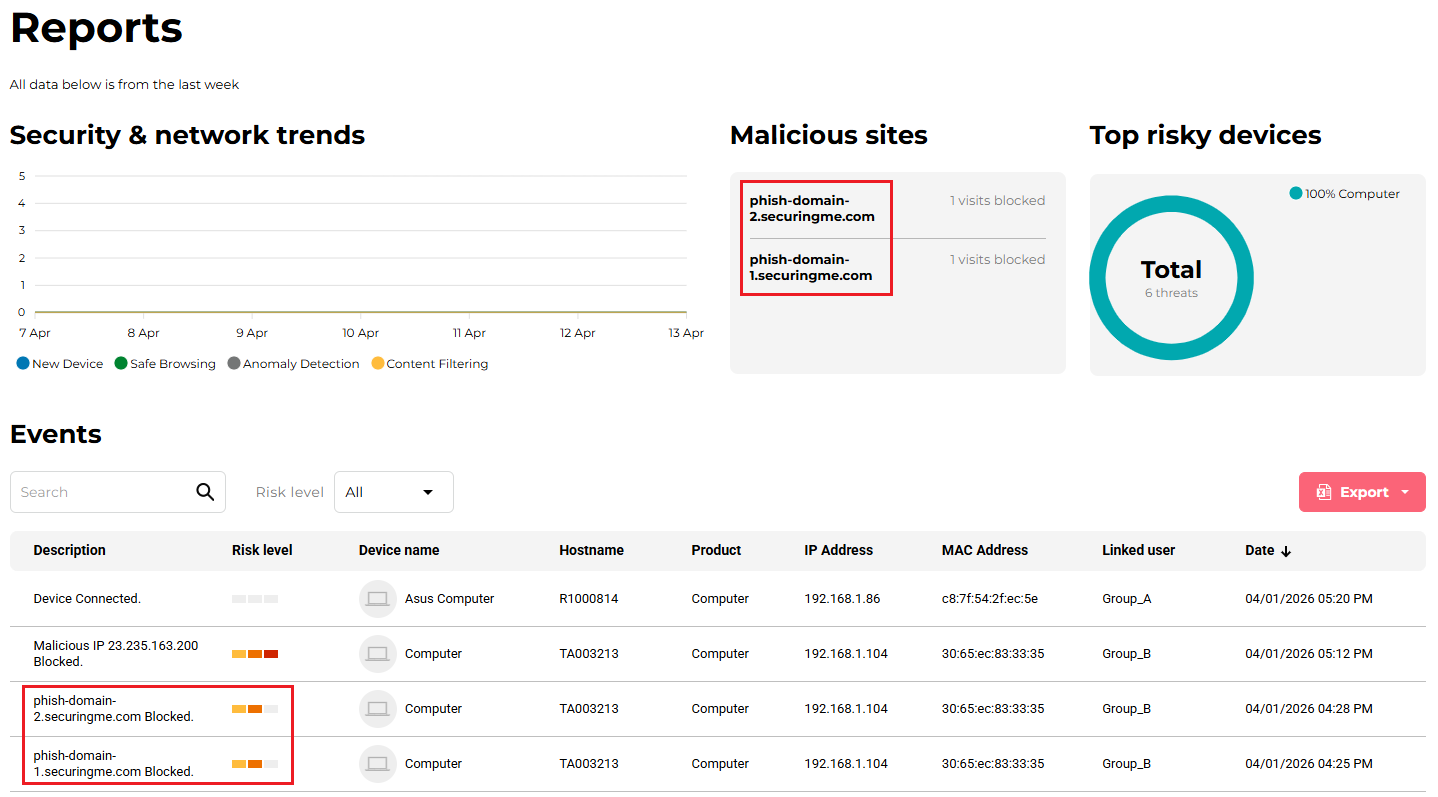
Through the Threat Protection cloud portal, administrators gain a centralized view of the network's security status and connected devices.
The Reports interface provides information on Security & Network Trends, Malicious Sites, Top Risky Devices and Security Events, including details such as risk level, device name, IP/MAC address, linked user, and event date and time.
This allows administrators to quickly identify blocked malicious IPs/domains, suspicious devices and security events, monitor network security trends and export relevant reports for further analysis.
Cloud-Based Threat Intelligence
Threat Protection is continuously enhanced through cloud-based threat intelligence and automatic security intelligence updates. Protection mechanisms and information about emerging threats are updated through the cloud, helping keep network protection up to date against evolving online threats.
Available Editions
Threat Protection SentryDesigned for SOHO, small business networks and branch offices. Supported Series: LAN Devices: up to 100 |
Threat Protection GuardianDesigned for SMBs and larger business networks. Supported Series: LAN Devices: up to 200 |
Both editions combine Edge Gateway Protection + Cloud Intelligence, with Sentry designed primarily for smaller networks and Guardian for larger SMB environments with a greater number of connected devices.
Easy Activation & Management
Threat Protection is integrated into supported DrayTek Vigor routers and does not require an additional security appliance or the installation of endpoint agents.
The subscription is activated through MyVigor / VigorShield using the corresponding License Key. Once activated on the router, access to the service's cloud portal is provided for centralized monitoring, configuration and reporting.
Security intelligence data is automatically updated through the cloud, simplifying day-to-day network security management.
Service availability and functionality depend on the Vigor router model and the installed firmware version.
| Datasheet DrayTek Threat Protection: | 
|
|---|